Vulnerabilities
SGLang Sandbox Escape in Dumper Endpoint Enables Remote Code Execution
A critical code injection flaw in SGLang versions up to 0.5.22 allows unauthenticated attackers to execute arbitrary Python code via the scheduler process.
Everything Firewall Chronicle has reported about code injection: 2 stories, newest first. Part of our Vulnerabilities coverage.
A critical code injection flaw in SGLang versions up to 0.5.22 allows unauthenticated attackers to execute arbitrary Python code via the scheduler process.
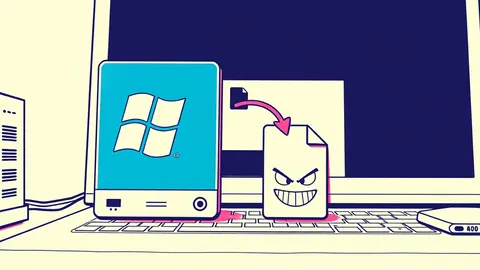
DLL hijacking exploits the predictable order in which Windows searches for libraries, allowing malicious code to run before legitimate components load.